InPractice: Project vs Enterprise

What It Is: Balancing priorities in medium- to large-scale organizations is complex, especially in a high-paced environment where speed-to-value is critical, but there is existing infrastructure and technical debt to consider

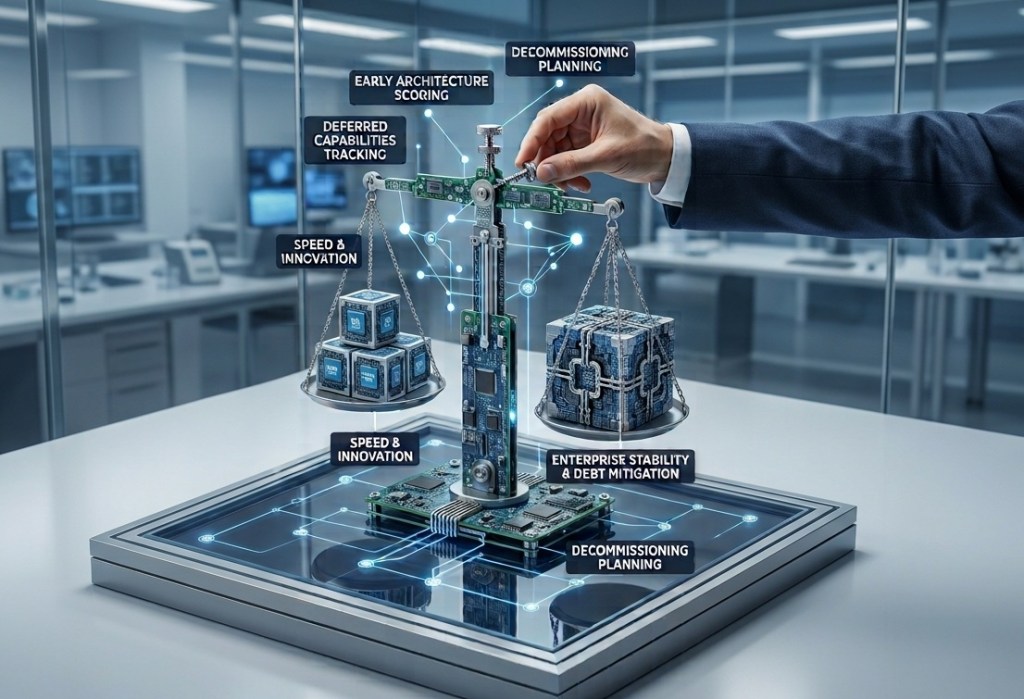
Why It Matters: Deferred decisions and the resulting complexity tend to slow an organization’s ability to remain agile and cost-effective over time.  Speed can come at a very heavy cost, and a balance should be struck that helps mitigate downstream risk while enabling quality delivery

Key Concepts

  • Have an enterprise blueprint and understand your leverage points
  • Engage architecture in scoping decisions early to understand and document tradeoffs
  • Estimate and plan time for important design decisions to mitigate downstream risk
  • Schedule deferred capabilities or track their impact to understand economic impact and debt
  • Explicitly account and plan for decommissioning solutions and technical debt reduction

Key Dimensions

A short anecdote

In my time as a CTO, I had a conversation with a partner proposing to use a market-leading database technology that was not in our existing footprint as part of a major upcoming program.

A few points:

  • The partner had implemented other work and not used this technology before in deference to ones we had in place
  • The platform was a market leader and good technology, so there was rationale to support why it could be a viable alternative
  • There was no capability gap to warrant why we had to use the new technology by comparison with existing technologies

I asked our partners what they would do, given that the decision would require us to expand our talent base to cover the new platform, integrate it with other data solutions, connect with our security tooling, manage identities and authorization across multiple back-end platforms, determine how to host, manage, and scale it from an infrastructure standpoint, etc.  No answers came back, just why it could be good for the project, but not for the company.  Ultimately, both things matter.


Having a blueprint

Project and product teams need to be able to execute in parallel to achieve any scale and efficiency, but doing so highlights the importance of having an enterprise blueprint and an appropriate level of standards to guide those efforts.  With the introduction of AI, the criticality of these things can’t be emphasized enough, for a multitude of reasons, not the least of which is maintaining a healthy security posture.

As a proponent of best-of-breed, component-based, and composable architecture, I don’t believe it is necessary to be overly prescriptive, but rather to identify boundaries across various business domains (sales, operations, finance, procurement, HR, etc.), the critical integration points that need to be standardized (it definitely isn’t “all of them”), core transactional, analytic, and master data, and the non-negotiables in terms of infrastructure and security.

Said differently, no one would build a new house without a blueprint that accounts for all the constituent elements, down to the plumbing and electrical wiring, yet it happens in technology all the time (sometimes at scale)… building without a design, and sometimes without a strategy… and the impact is cost, complexity, and risk.  Eventually that hinders agility and competitive advantage.


Engaging architecture in scoping

Aside from having an overall blueprint and some level of actionable standards, engaging an architecture capability early in the scoping process should help to surface leverage points and opportunities to align new delivery solutions to the strategy where possible. 

This is a careful balance to strike, because typically the front-end of the ideation and planning process, especially for critical programs, can move quickly with a significant number of stakeholders involved.  If the architecture team slows that process or approaches discussions in a way that feels cumbersome or “ivory tower”, the impact they have can be marginalized very quickly.  By comparison, if the team helps to identify opportunities for reuse, leverage of capabilities that will accelerate delivery, and ways to avoid decisions that could cause significant rework or downstream cost, there will be business value created in the process.


Estimating and allowing time for decisions

I remember a situation where a team was running a $100M+ multi-year program and reached a point mid-design where they announced, “we have a week to make the integration decision”.  A multi-year program.  A week to make a critical infrastructure decision…. and the team’s response to any challenge was that the cost of extending the program and/or missing the delivery dates mandated that the decision be made that quickly.

As it happened, the program was delayed for many other reasons downstream and the integration choices led to high operating cost, but the point is that critical decisions need time to be evaluated and possibly proven out through proofs-of-concept.  The greater the knowledge risk or cutting edge the solution is, the more time that probably should be accounted for to ensure the solution will perform and scale as expected (if it is a strategic effort). 

The alternate delivery approach is to “fail fast” and test out small pilots to learn what does and doesn’t work, but I’ve seen many of these efforts fail to scale and integrate over time because of a fundamental lack of design and architecture.  Fast does not need to mean a lack of process and discipline, but that can be the tradeoff that is made at times.


Managing “deferrals”

Having spent most of my career delivering solutions, I am biased towards action and making difficult decisions where tradeoffs on speed versus quality need to be made.

That being said, deferred decisions tend to become technical debt, so I believe it is a good thing to maintain active transparency on issues that should be remediated as part of an ongoing simplification and modernization effort.  Where these decisions are too tightly coupled with a program or solution, they almost always get deprioritized in deference to new features or capabilities, and no one typically wants to invest in “infrastructure” when something “works” at a functional level.


Planning the cleanup

In a similar way, when planning is too project-centric, the focus can be entirely on deployment of new capabilities without properly addressing the decommissioning of existing solutions that were previously in place, that can be a material effort, and not doing so can result in hidden complexity, inefficiency, and cost. 

The remedy is fairly simple in this case, which is to ensure that the list of existing solutions to be replaced or retired is included in the project/program scope, roadmap, and plan.  Where this is not in place, there is risk that things will be missed and additional complexity created post-deployment.


Wrapping Up

Balancing speed and quality/resilience is a continual challenge in technology, especially with the advent of AI.  Discipline isn’t about moving slowly, it’s about moving thoughtfully, acting locally, but thinking globally in terms of implications.

It may not be a substantial change to have a more deliberate balance in what benefits a project versus the enterprise, but a simple matter having just enough of the right activities in the right places as the right time.

For Additional Information: Fast and Cheap, Isn’t Good, On “Delivering at Speed”

Excellence doesn’t happen by accident.  Courageous leadership is essential.

Put value creation first, be disciplined, but nimble.

Want to discuss more?  Please send me a message.  I’m happy to explore with you.

-CJG 09/29/2026
InPractice: Unpacking Enterprise-level AI

What It Is: “Enterprise-level AI” is an expression that is coming up more in discussion right now.  Conceptually, there is a clear distinction between what this likely means (i.e., NOT a set of AI “pilots” or “experiments”), but the definition beyond that feels extremely vague.

Why It Matters: We are in a time that has a lot of similarity to the dotcom era, where new technologies offered the promise of significant business transformation and competitive differentiation, but without necessarily a clear line-of-sight to how that will be accomplished.  Organizations with a defined and thoughtful strategy will capitalize on these capabilities faster and more effectively than those who don’t.

Key Concepts

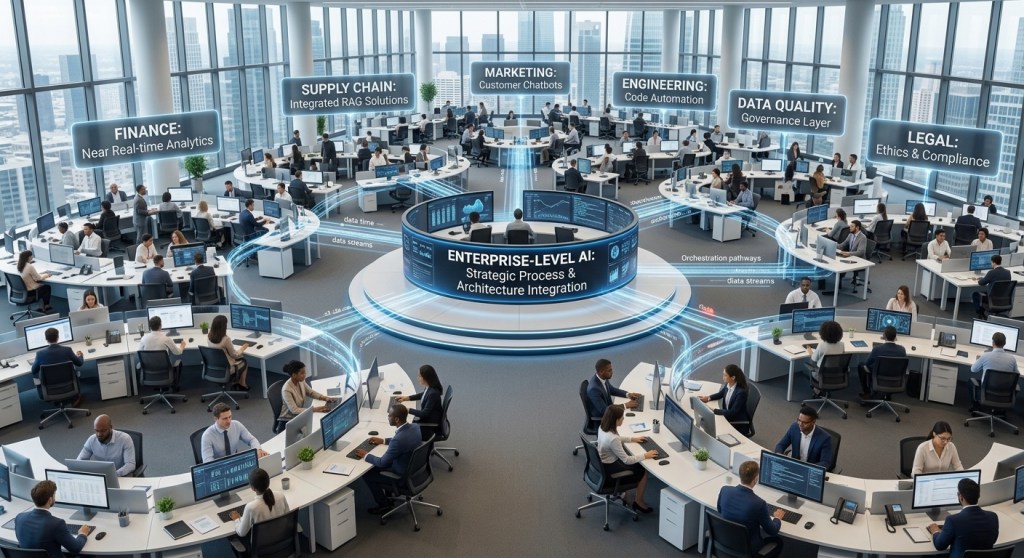
  • AI needs to be an integrated element of a business strategy.  It’s not about the tools
  • Capitalizing on the latest technologies places a strong emphasis on process and architecture
  • Governance is critical to ensuring compliance, privacy, security, ethical, and other critical considerations are factored in “up front” to manage exposure once the technologies start being used in production settings

Unpacking the Definition

Use Cases

The phrase Enterprise-level AI itself is understood to express a concept of “done this at scale”, but what exactly does that mean?

If we had an example checklist of platform-level AI-related capabilities in production:

  • AI/ML solutions providing near real-time analytics
  • Implemented a SaaS application that has “AI features”
  • Deployed automation/robotics solutions with PhysicalAI capabilities
  • Running Microsoft Office 365 with Copilot enabled
  • Providing access to one or more LLMs (ChatGPT, Claude, etc.) with guidelines on acceptable use
  • Implemented an AI-enabled customer service or internally focused chatbot
  • Ingested a set of documents into a knowledgebase that can be queried using natural language
  • Enabling Amazon Q to provide personal productivity capabilities to end users
  • Leveraging Claude or other similar tools to automate software development or testing
  • Deploying vibe coded applications or allowing end users to develop their own solutions via a platform
  • Implementing domain- and company-specific RAG solutions to leverage internal data along with a foundation model to fuel competitive advantage or differentiation
  • Exposing agentic capabilities to automate activities that drive productivity, efficacy, quality, etc.
  • Integrating agentic and orchestration capabilities to optimize transaction routing and drive process efficiency

This list isn’t meant to be exhaustive, but arguably everything above qualifies as a potential use of AI in an organization today.  So, what does Enterprise-level AI mean?

Is it all of the above, some subset, a percentage or ratio of them?  If it can mean “any of the above”, then probably nearly everyone working in technology for the last 10 years can claim they’ve implemented AI, and that stops being a differentiator worth discussing.


What’s Missing…

Ok, so I just leaned in on where I believe most people conceptually go with this topic, which is straight to the implementations… but that leaves a LOT out.

What about how these solutions enable and fit with your business and technology strategy?

How are you governing them to ensure you don’t expose customer privacy data, create platforms that waste end-user time creating redundant capabilities, allow malicious code or prompts, keeping track of all the tools in place so licensing compliance (and costs) don’t become issues, etc.?

How are you integrating these efforts, prioritizing, and measuring their value in concert with other technology efforts?

How are you thinking about agents in relation to existing user/roles/personas and workflows?  Are they something integrated, something entirely independent, or a combination of both?

Do you have the underlying process and technology infrastructure to enable any or all of the above use cases at scale?

Can you change from one of your chosen AI technologies to a “newer alternative” with minimal business disruption?

Do you have the data governance and data quality mechanisms to ensure insights generated via an AI-enabled solution are valid?

From my point of view, this is what Enterprise-level AI actually is: A disciplined process and infrastructure to identify, prioritize, develop, introduce, and govern AI investments as part of your overall IT portfolio. 

With the appropriate operating environment, the nature of the use cases becomes secondary, and the focus is on value creation and business enablement, not the technology being used.


Wrapping Up

There was a time when organizations rushed to invest heavily in the internet and ways it could create competitive advantage.  A lot of money was invested, often with less-than-ideal outcomes, and a significant market contraction occurred until we identified the places the technologies made sense, they matured somewhat, and they became more integrated with our organizational DNA.

In the twenty-five years since that time, we have figured most of that out.  We generally don’t have separate “eBusiness” teams, projects involving web or internet technologies are included naturally with project portfolios and whatever prioritization processes exist, we ask the value questions (ideally) up front, and we think about delivering solutions across mobile and web platforms without any thought.

There will be a point in time where AI-driven solutions cross over from being interesting and cool experiments to just another way we do our work, and the sooner we start thinking in a more systemic, organized way about how they affect what we do, the better.

The opportunity is there.  The question is whether we’ll put strategy high enough on the list of priorities to transform our aspirations to meaningful outcomes.

I hope the ideas were helpful.  As always, feedback and reactions are welcome.

Excellence doesn’t happen by accident.  Courageous leadership is essential.

Put value creation first, be disciplined, but nimble.

Want to discuss more?  Please send me a message.  I’m happy to explore with you.

-CJG 09/14/2026

InPractice: Unpacking IT Assessment

What It Is: Understanding the current state of IT within an organization requires a thoughtful process for evaluating how it is structured, aligned, and operating in concert with business needs and expectations.  That process is typically referred to as an “IT Assessment”, where an outside reviewer or firm provides perspective on how an IT organization is performing and recommended actions to drive improvement.

Why It Matters: One of the benefits and challenges of working within technology has always been the continuous change and complexity that comes with trying to deliver advanced capabilities to meet business needs and drive competitive advantage, while doing so at speed, securely and reliably, and with quality.  Even the most performant organization has opportunities to improve, and the value in IT Assessment is to provide a line of sight to where the organization is and opportunities to improve in the interest of continuing to drive excellence in the value and quality of service delivered.

Key Concepts

There are three fundamental pillars around which IT excellence should be evaluated, they are:

  • Business Enablement – how well IT capabilities align and support business needs
  • Delivery Excellence – how well the IT organization delivers and manages the technology footprint in place to support and enable the business
  • Operational Excellence – how healthy and well-managed the IT organization is from an operating perspective, irrespective of delivery execution and the technology footprint itself

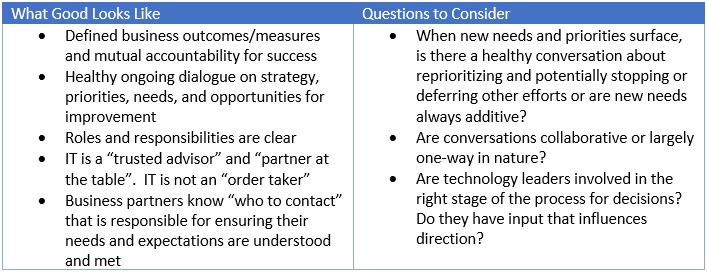
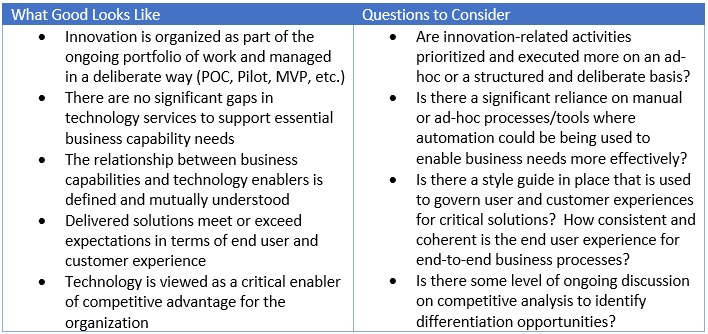
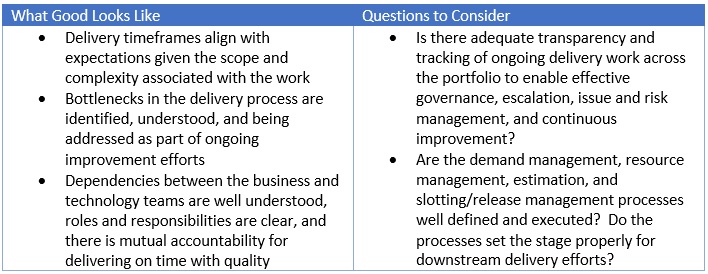
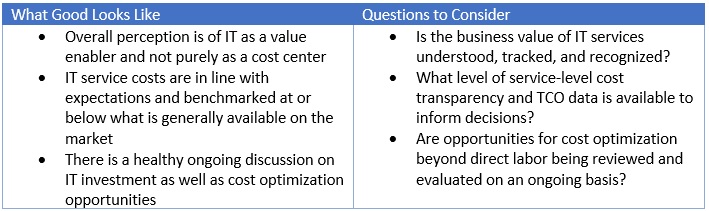
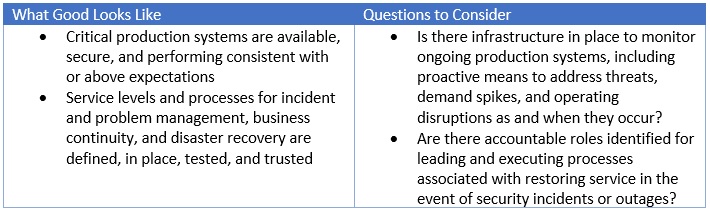
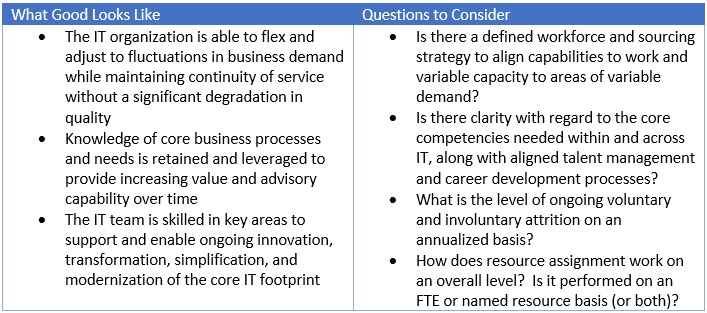
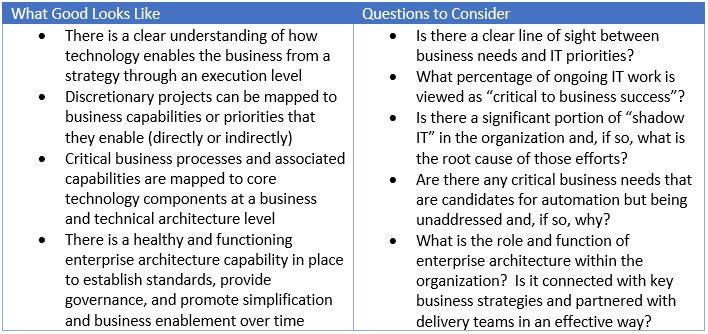
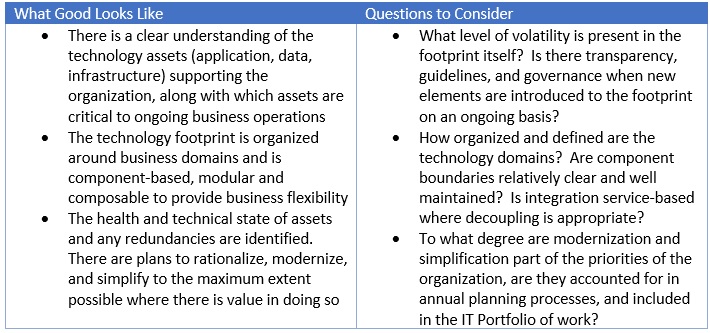
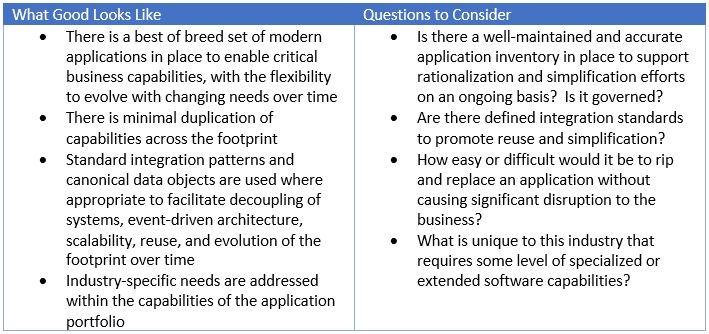
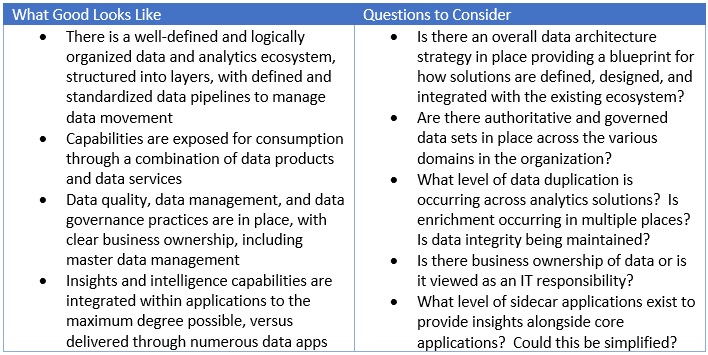
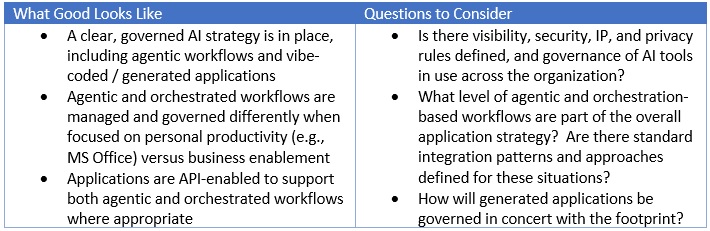
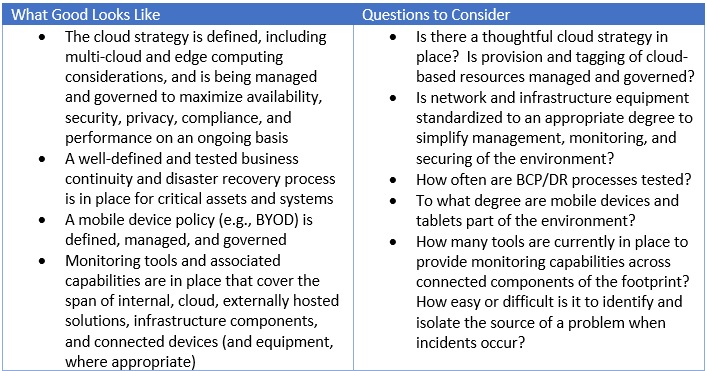
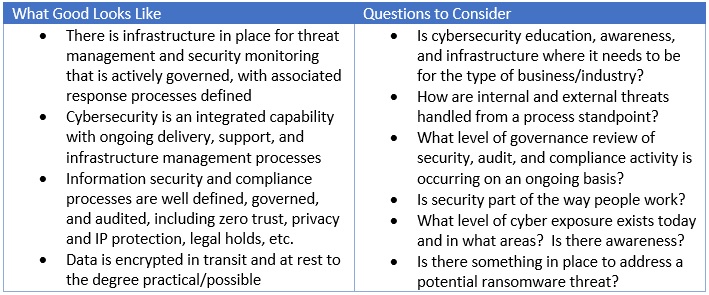
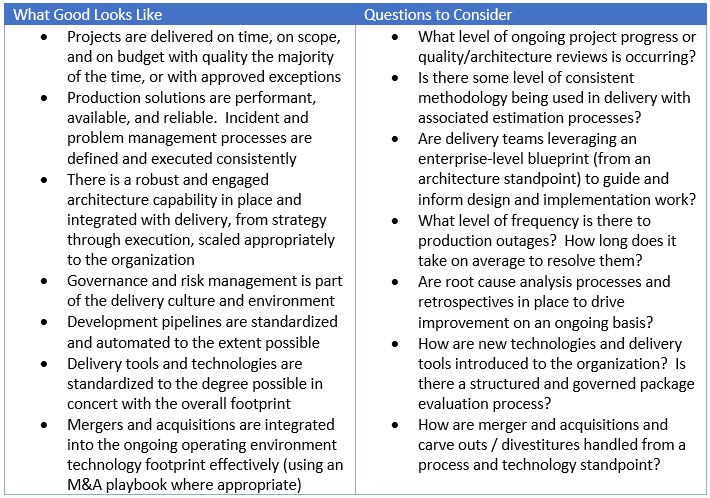
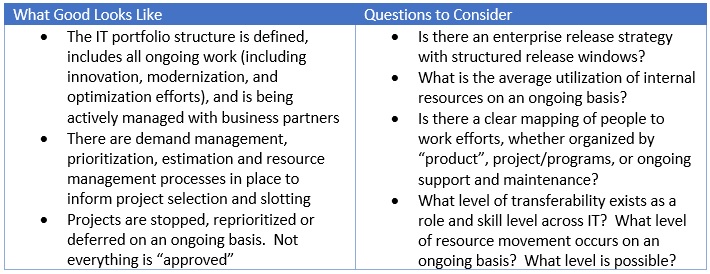
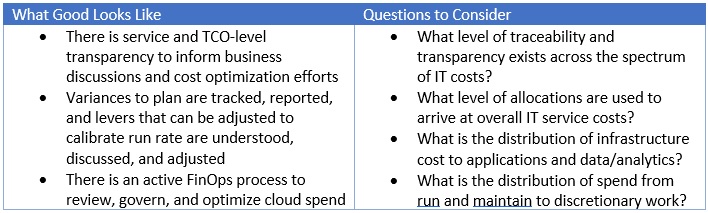
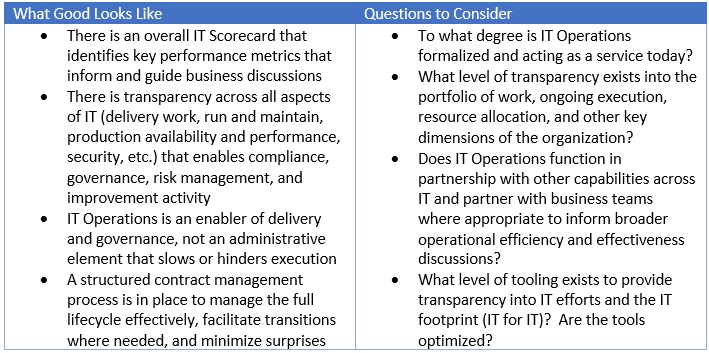
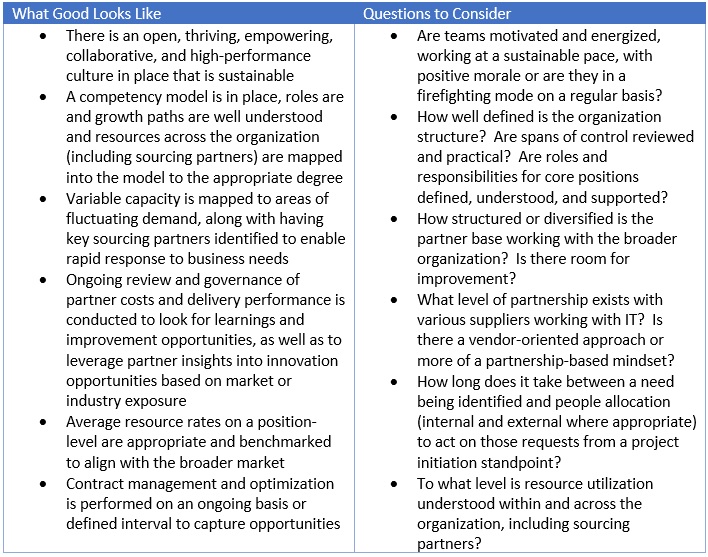
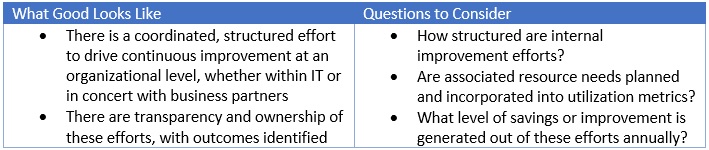
The remainder of this article will be focused on nineteen dimensions across these three pillars, in the interest of both defining “What Good Looks Like” in each dimension (in a perfect world) and some key “Questions to Consider” in each case, as a means to explore the current situation. 

It is worth noting that there are and will be industry-specific considerations that come into play beyond what is identified below, but “IT is IT” to a degree, regardless of industry, and I would argue that most or all of what is listed below should apply to the vast majority of technology organizations.  The model can and should be extended where appropriate to address an such considerations where it is important to do so.

The considerations themselves are also top-of-mind items, but not meant to be exhaustive, as secondary areas of exploration would tend to surface through the process of understanding and discussing the dimensions below.  Hopefully this is a good start… feedback is certainly welcome where something significant may have been missed.

Business Enablement

Partnership and Accountability

Innovation / Capability Enablement / Competitive Advantage

Speed-to-Value

Value / Cost Ratio

Reliability, Security, and Performance

Agility, Capability, and Continuity

Delivery Excellence

Business-Aligned Technology Strategy

Technology Footprint

Applications

Data and Analytics

AI, Agentic, and Orchestration

Cloud, Infrastructure, and Monitoring

Security, Audit, and Compliance

Delivery Management

Operational Excellence

Portfolio Management

Financial Management

IT Operations

Workforce and Sourcing Strategy

Continuous Improvement

Wrapping Up

There are many elements that influence achieving excellence with IT and it is a given that no environment would match up to the “perfect world” that is described across the dimensions above and that’s completely fine. The point is to aspire to achieve excellence, then have a strategy and plan to continuously head in the right direction.  Where we don’t have a plan or aren’t focused on improving what we do on a day-to-day basis, the odds are that we won’t do it or won’t achieve sustainable improvements over time.  I hope the information was helpful and thought-provoking.

For Additional Information: InBrief: IT Excellence, Culture and Sustaining Success, InBrief: Developing IT Strategy, InBrief: Transformation, InBrief: IT Value/Cost Optimization, InBrief: The Intelligent Enterprise 2.0, InBrief: The Role of Architecture, InBrief: IT Portfolio Management, InBrief: IT Operations, InPractice: PMOs and Governance, InBrief: Workforce and Sourcing Strategy, InBrief: Intelligent Monitoring

Excellence doesn’t happen by accident.  Courageous leadership is essential.

Put value creation first, be disciplined, but nimble.

Want to discuss more?  Please send me a message.  I’m happy to explore with you.

-CJG 05/31/2026

InBrief: Defining Manufacturing Maturity

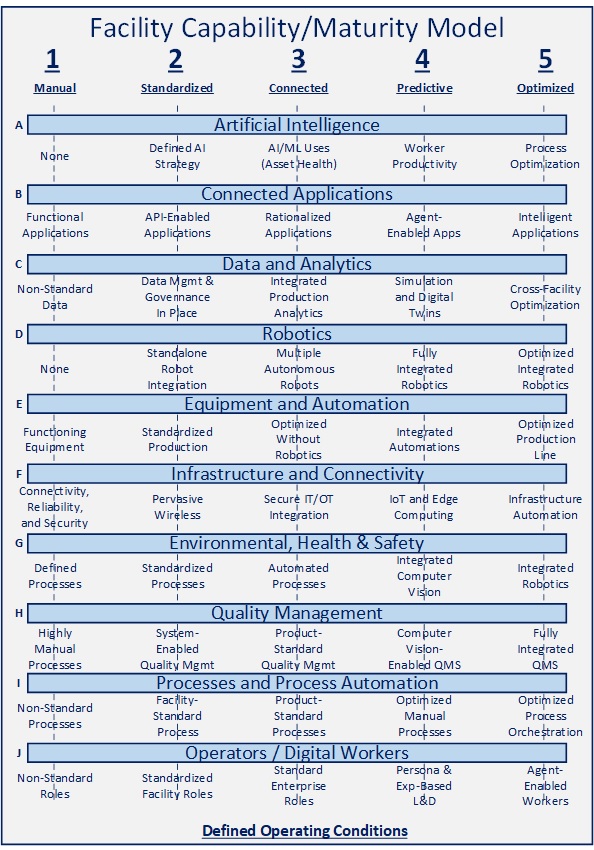
What It Is: Many models have been developed over the years to describe the factory environment and its structure and maturity, for various reasons, from the Purdue model to Industry 4.0.  The purpose of this summary article is to share a concept on how to unpack and discuss the evolution of a facility across multiple dimensions.  It is not meant to be prescriptive or “correct” from a content standpoint.  It is intended to be used as a tool to inform a structured conversation

Why It Matters: As we continue to add elements to the manufacturing environment, whether it is additional monitoring through sensors, automation through robotics, or analytics leveraging more powerful AI models, our ability to be disciplined and intentional in how we not only define our desired/”ideal” future state but also measure and map out our transition is critical in reaching those desired outcomes efficiently and in a cost-effective way

Key Concepts

  • Given the complexity and layers of process and automation involved, the “optimized” digital factory of the future needs to be architected, not just engineered
  • The diagram above is a representation meant to enable a structured discussion on the various operating dimensions that are important in the environment, some of which may not apply at all, depending on the nature of the manufacturing process and goals of the organization
  • The goal of the model is to break down the people, process, equipment, and technology dimensions (similar to the SIRI model from 2017) into relevant components and identify what a reasonable maturity curve looks like independent of other aspects of a facility.  That maturity process could vary significantly by organization (or by product/facility), but the overall goal would be to identify meaningful states along a continuum from unstructured and non-standard ways of working to those that are more standardized, supported through automation, and optimized to the extent possible
  • Through discussion of the various dimensions, a common vision and understanding can be reached in terms of “what good looks like” that is much more actionable and critical dependencies can be identified to help inform the prioritization of efforts that would be part of a modernization journey (e.g., the criticality of infrastructure to enable digital capabilities)
  • With a general framework established, one or more “transition states” could be identified to create meaningful tollgates along an evolutionary journey towards whatever the desired state is, assuming more than one step may be required over a period of time
  • Once the framework is defined, it could be used to establish a baseline of where a given facility is along the maturity curve, the “ideal” state, and any transition states and efforts that would be part of evolutionary journey as part of an overall, integrated transformation strategy
  • Operating benchmarks could also be established for each of the transition states to evaluate performance across a set of facilities to look for additional opportunities for improvement
  • In short, the transformation journey could be described as identifying the maturity curve and desired operating states, mapping the current state of facilities against the framework, then developing a roadmap for modernizing each facility (where required) as part of an overall transformation effort  

For Additional Information: InBrief: Digital Manufacturing

Excellence doesn’t happen by accident.  Courageous leadership is essential.

Put value creation first, be disciplined, but nimble.

Want to discuss more?  Please send me a message.  I’m happy to explore with you.

-CJG 03/16/2026

InBrief: Intelligent Monitoring

What It Is: There is an opportunity to rethink how we approach monitoring of operations, to better understand dependencies across components, proactively surface risks to avoid issues, and more effectively manage incidents when they occur

Why It Matters: The complexity of operations, particularly in Manufacturing, has increased substantially, both due to the introduction of digital capabilities and automation at facilities, as well as movement to a hybrid cloud environment.  That complexity makes the effective identification of issues time consuming, which can cause significant and costly disruption to production and operating efficiency

Key Concepts

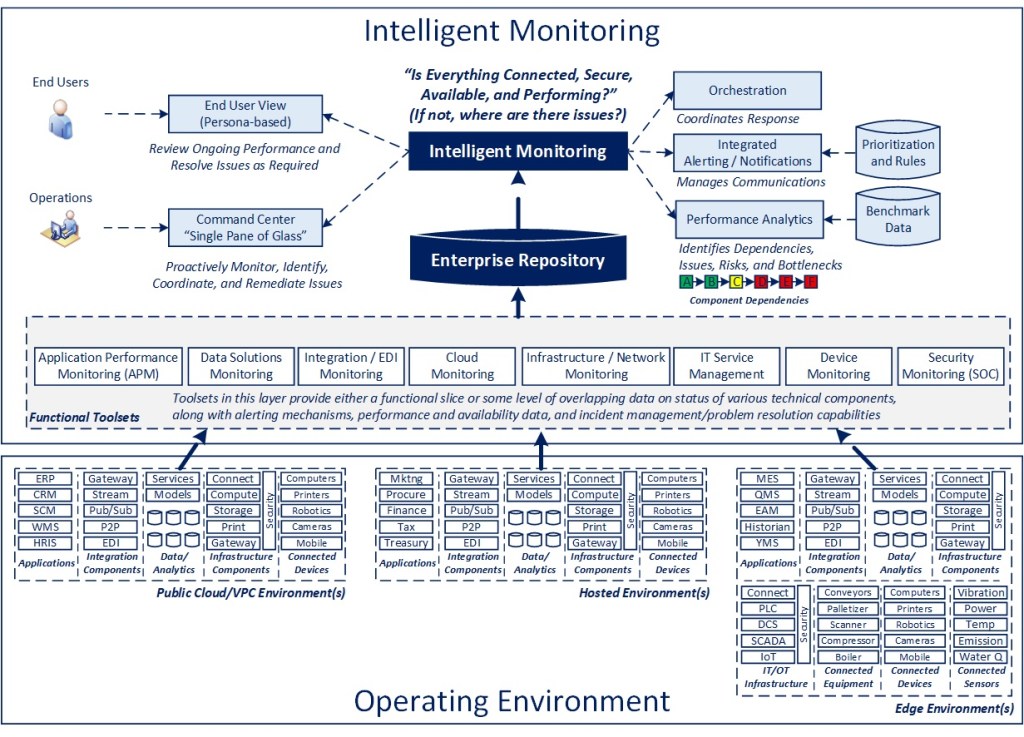
  • Define a conceptual framework for how your environment is organized first, along with what elements are important to monitor in an integrated fashion
  • Review existing toolsets in the market (cloud, APM, infrastructure monitoring) to determine whether they provide adequate capability to identify and manage issues effectively.  If so, there may be no business reason to look any further
  • If the complexity of the environment is such that there are a considerable number of critical components involved, the tools available don’t provide sufficient capability, and the cost of extended outages or inadequate operating performance is material… THEN it may make sense to explore a more integrated and intelligent solution
  • It is important to note that this is not an either/or proposition.  Even when pursuing a more elegant and integrated solution, for certain roles (e.g., security monitoring), existing tools likely should be leveraged in parallel with more advanced tools, so as not to need to replicate capabilities available across other tools that may be in place
  • The goal is to aggregate data from across existing monitoring platforms (or from source components themselves), run analytics to determine dependencies across operating components, and then apply that understanding to both monitor and triage issues more effectively at the time of an incident, as well as to handle the resolution process more effectively by having a streamlined process for notification and problem resolution
  • Once the infrastructure is established to perform the base capabilities described herein, additional components and data sets could be added over time to enrich the capability overall

Key Dimensions of the Solution

  • Enterprise Repository – Aggregated availability, connectivity, performance, and security data
  • Intelligent Monitoring – An AI-informed process that identifies risks and accelerates resolution
  • Performance Analytics –AI capability that identifies dependencies and evaluates benchmarks
  • Integrated Alerting / Notifications – Process to reduce duplication and manage communication
  • Orchestration – Workflow rules for incident management depending on the existing conditions
  • Command Center – A holistic view of operations across connected solution components
  • End-User View – A subset of enterprise data, specific to the end user relevant to their need/role


For Additional Information: InBrief: The Intelligent Enterprise 2.0, InBrief: Digital Manufacturing, InBrief: IT Operations


Excellence doesn’t happen by accident.  Courageous leadership is essential.

Put value creation first, be disciplined, but nimble.


Want to discuss more?  Please send me a message.  I’m happy to explore with you.

-CJG 03/03/2026

InBrief: The Role of Architecture

What It Is: Architecture provides the structure, standards, and framework for how technology strategy should be manifested and governed, including its alignment to business strategy, capabilities, and priorities.  It should ideally be aligned at every level, from the enterprise to individual delivery projects

Why It Matters: Technology is a significant enabler and competitive differentiator in most organizations.  Architecture provides a mental model and structure to ensure that technology delivery is aligned to overall strategies that create value.  Having a lack of architecture discipline is like building a house without a blueprint… it will cost more to build, not be structurally sound, and expensive to maintain

Key Dimensions

  • Operating Model – How you organize around and enable the capability
  • Enable Innovation – How you allow for rapid experimentation and introduction of capabilities
  • Accelerating Outcomes – How you promote speed-to-market through structured delivery
  • Optimizing Value/Cost – How you manage complexity, minimize waste, and modernize
  • Inspiring Practitioners – How you identify skills, motivate, enable, and retain a diverse workforce
  • Performing in Production – How you promote ongoing reliability, performance, and security

Operating Model

  • Design the model to provide both enterprise oversight and integrated support with delivery
  • Ensure there is two-way collaboration, so delivery informs strategy and standards and vice versa
  • Foster a “healthy” tension between doing things “rapidly” and doing things “right”

Innovate

  • Identify and thoughtfully evaluate emerging technologies that can provide new capabilities that promote competitive advantage
  • Engage in experimentation to ensure new capabilities can be productionized and scaled

Accelerate

  • Develop standards, promote reuse, avoid silos, and reduce complexity to enable rapid delivery
  • Ensure governance processes promote engagement while not gating or limiting delivery efficacy

Optimize

  • Identify approaches to enable simplification and modernization to promote cost efficiency
  • Support benchmarking where appropriate to ensure cost and quality of service is competitive

Inspire

  • Inform talent strategy ensuring the right skills to support ongoing innovation and modernization
  • Provide growth paths to enable fair and thoughtful movement across roles in the organization

Perform

  • Integrate cyber security throughout delivery processes and ensure integrated monitoring for reliability and performance in production, across hosted and cloud-based environments


For Additional Information: Enterprise Architecture in an Adaptive World, InBrief: The Intelligent Enterprise 2.0, The Future of IT


Excellence doesn’t happen by accident.  Courageous leadership is essential.

Put value creation first, be disciplined, but nimble.


Want to discuss more?  Please send me a message.  I’m happy to explore with you.

-CJG 02/12/2026

InBrief: Transformation

What It Is: Transformation is the process of reshaping a way of working in the interest of achieving a significant and measurable impact in business results

Why It Matters: When faced with changing market conditions, competitive threats, technology advancements, etc., it is critical for organizations to reinvent themselves.  This typically involves changes to process, organization, and technology and doing so in a thoughtful manner is critically important

Critical Dimensions

  • A Compelling Vision – The desired future state should be clear enough to create emotional investment and the commitment required to overcome the inertia that naturally resists change
  • Clear Business Outcomes –There should be tangible goals established (along with key financial and operating metrics) to inform prioritization and guide critical decisions throughout execution
  • Courageous, Committed Leadership – Transformation efforts are complex and require resilience, decisiveness, persistence, and determination to work through adversity along the way
  • A Supportive Culture – The environment and culture within an organization will have an impact on the degree of change that is possible to achieve overall and the rate at which it can be done
  • A Thoughtful Approach – It is tempting in larger programs to initiate too much work, too quickly, causing significant disruption and suboptimal results (or even programs to fail overall).  Given that a lot of learnings tend to occur in terms of processes, standards, and governance in initial delivery efforts, it is often the case that incubating large programs with a smaller, expert team and extending and scaling afterward is a more effective way to build momentum and reduce risk
  • Results-Orientation – Another problem in large transformation efforts is taking on too much, too early in terms of scope that can substantially defer any benefit realization, by comparison with a consistent, incremental delivery environment that is both predictable and repeatable over time
  • Adaptability and Agility – Transformation efforts are messy, involve complexity, and typically run into a host of issues throughout execution.  It is critical to maintain a high level of transparency into ongoing work, have an active and engaged governance process, and to make decisions efficiently and thoughtfully as they are needed during execution.  Roadmaps produced at the start of large programs rarely remain unchanged for very long, and it’s important that every inflection point is taken as an opportunity to learn, improve, and respond versus react
  • Patience and Discipline – Sustainable change takes time.  While it’s possible to force a level of change in the short-term and achieve incremental benefits, systemic and holistic changes to the way an organization operates take time.  Managing the process in a disciplined way both helps achieve overall results faster as well as mitigate risk


For Additional Information: The Seeds of Transformation, The Criticality of Culture, On “Delivering at Speed”


Excellence doesn’t happen by accident.  Courageous leadership is essential.

Put value creation first, be disciplined, but nimble.


Want to discuss more?  Please send me a message.  I’m happy to explore with you.

-CJG 01/28/2026

InBrief: CIO and CTO Roles

What It Is: Technology organizations are sometimes led through a combination of CIO and CTO roles, working towards a shared vision, each having a clear focus in the interest of promoting IT excellence

Why It Matters: Technology continues to advance at a rate, particularly with the introduction of AI, that exceeds many organizations ability to respond effectively.  Having the right leadership in place to develop strategy, consider longer-term implications of decisions made in ongoing delivery, and govern execution can be key to avoiding technical debt, while promoting delivery excellence over time

Five Types of CTOs

  • Technology Strategist – This is the most common modern orientation, focused on enablement, simplification, optimization, and capability delivery
  • Mistitled CIO – This occurs when the CTO actually has all the typical CIO responsibilities and they are fulfilling that role in every way, leading IT, setting direction, etc. without the CIO title
  • Futurist – This occurs where the CTO plays a more directional, but not action-oriented role, focused on white/position papers, and ideation
  • Infrastructure Lead – This is the historical role of a CTO, focused more on hosting, networking, reliability, performance, and operations with the CIO covering applications and data
  • Lead Designer / Senior Developer – This generally the case in start-up/smaller scale product environments, where the CTO leads the product design and helps code the solution

High-Level Differences

  • CIO focuses on the “what”, obtains business alignment and identifies capabilities, along with desired technology capabilities, focuses on the customer and providing vision and direction
  • CTO focuses on the “how”, understands desired business capabilities, determines how to provide technical capabilities and deliver on commitments, partnering with the broader team
  • Both roles participate in governance, CIO provides and aligns business priorities, CTO provides and aligns technical priorities in support of the CIO

When It Makes Sense to Have a CTO in Addition to a CIO

  • There is sufficient time required working with business partners that additional support is needed to define and evolve the technology strategy and work actively with delivery leaders
  • There is considerable complexity in the technology footprint, a high degree of transformation, or substantial integration required across ongoing delivery where having the CIO focused in the weeds of execution could result in underserving the business team and executive leadership
  • There is a need to move multiple levers (cloud platform migration, modernization, core platform implementation, AI integration, etc.) that a level of dedicated focus and oversight is needed to work through the risks and impacts of various strategies to define the best technology solution
  • When the scale of the organization in people, internally, externally, including customers, suppliers, and partners exceeds one person’s ability to manage relationships effectively
  • Where the CIO has a business background and it is helpful to supplement their capabilities with a more technology-focused leader overall

Benefits of Having a “Healthy Tension”

  • There can be a natural tension created when there is a separation of roles, because a CIO generally is incented to deliver new business capabilities at speed and the CTO should be incented to do things “right” to minimize long-term cost of ownership, managing technical debt, promoting standards and governance, and improving predictability of the delivery environment
  • Business delivery will generally be top priority, but having a CTO can mitigate the impact of tradeoffs made during delivery, particularly in large programs, where consequences are higher

The Downside:

  • There is incremental cost associated with adding leadership roles, there can be confusion across the broader IT leadership if roles and responsibilities aren’t clear, and a strong CIO/CTO partnership is important to making the role effective in practice
  • That being said, the value to any organization with a relatively large technology footprint would likely far exceed the cost of having a CTO focused on managing complexity and optimizing cost

The Difference Between CTO and Chief Architect

  • The CTO is the keeper of the overall technology strategy, apps, data, infrastructure, security integration with all of the above (working with the CISO), inclusive of the delivery environment
  • A “Chief Architect” tends to be more narrowly focused on application and data architecture strategy, but with awareness on how to incorporate cloud and platform strategy as well
  • A Chief Architect could be a role reporting to the CTO, depending on the scale of the organization, focused more on defining, modernizing, or rationalizing the enterprise ecosystem of connected components, acting more like a designer than a strategist, where a CTO without this role would generally do both at the enterprise level


For Additional Information: InBrief: IT Excellence, Fast and Cheap, Isn’t Good


Excellence doesn’t happen by accident.  Courageous leadership is essential.

Put value creation first, be disciplined, but nimble.

Want to discuss more?  Please send me a message.  I’m happy to explore with you.

-CJG 01/17/2026

InPractice: PMOs and Governance

What It Is: Governance (in a delivery context) is the process for reviewing a portfolio of ongoing work in the interest of enabling risk management, containing avoidable cost, and increasing on-time delivery.  PMOs (Project/Program Management Offices) are the mechanism through which governance is typically implemented in many organizations.Why It Matters: As the volume, risk, and complexity in a portfolio increase, there is typically a disproportionate increase in issues that come about, leading to cost overruns, missed expectations on scope or schedule (or both), and reduced productivity.  PMOs, meant to be a mechanism to mitigate these issues, are often set up or executed poorly, becoming largely administrative and not value-generating capabilities, which furthers or amplifies any underlying execution issues.  In an environment where organizations want to transform while managing a high level of value/cost efficiency, a disciplined and effective governance environment is critical to promoting IT excellence

Key Concepts

  • There are countless ways to set up an operating model in relation to PMOs and governance, but the culture and intent have to be right, or the rest of what follows will be more difficult
  • There is a significant difference between a “governing” and an “enabling” PMO in how people perceive the capability itself. While PMOs are meant to accomplish both ends, the priority is enabling successful, on-time, quality delivery, not establishing a “police state”
  • Where the focus of a PMO becomes “governance” that doesn’t drive engagement and risk management it can easily become an administrative entity that drives cost and doesn’t create value and ultimately undermines the credibility of the work as a whole
  • The structure of the overall operating model should align to the portfolio of work, scale of the organization, and alignment of customers to ongoing projects and programs
  • It can easily be the case that the execution of the governance model can adapt and change year-over-year but, if designed properly, the structure and infrastructure should be leverageable, regardless of those adjustments
  • The remainder of this article with introduce a concept for how to think about portfolio composition and then various dimensions to consider in creating an operating model for governance

Framing the Portfolio

In chalking out an approach to this article, I had to consider how to frame the problem in a way that could account for the different ways that IT portfolios are constructed.  Certainly, the makeup of work in a small- to medium-size organization is vastly different than a global, diversified organization.  It would also be different when there are a large number of “enterprise” projects versus a set of highly siloed, customer-specific efforts.  To that end, I’m going to introduce a way of thinking about the types of projects that typically make up an IT project portfolio, then an example governance model, the dimensions of which will be discussed in the next section.

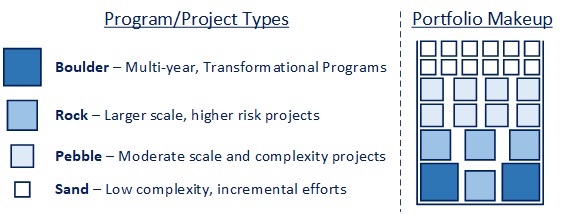
The above graphic provides a conceptual way to organize delivery efforts, using the rocks, pebbles, and sand in a jar metaphor that is relatively well known, and also happens to apply to organizing technology delivery.

To establish effective governance, you generally first want to examine and classify delivery projects/programs based on scale (in effort and budget), risk, timeframe, and so on.  This is important so as not to apply a “one size fits all” approach to how you track and govern projects that encumbers lower complexity efforts with the same level of reporting that you would typically have on larger-scale, transformation programs.

In the model above, I went with a simple structure of four project types:

  • Sand – very low risk projects that can be something like a rate change in Insurance or data change in analytics
  • Pebbles – medium complexity work like incremental enhancements or an Agile sprint
  • Rocks – something material, like a package implementation, new technology introduction, product upgrade, or new business or technology capability delivery
  • Boulders – high complexity, multi-year transformation programs, like an ERP implementation where there are multiple material, related projects under one larger delivery umbrella

The characteristics of these projects and metrics you would ideally like to gather, along with the level of “review” needed on an ongoing basis would vary greatly, which will be explored in the next section. 

In a real-world scenario, it is possible that you might want to identify additional sub-categories to the degree it helps inform architecture or delivery governance processes (e.g., security, compliance, modernization, AI-related projects), most of which would likely be specialized kinds of “Pebbles” and “Rocks” in the above model.  It is very easy to become bloated quickly in terms of a governance process, so I am generally a proponent of tuning the model to the work and asking only questions relevant to the type of project being discussed.

What about Agile/SAFe and Product team-oriented environments?  In my experience, it is beneficial to segment delivery efforts because, even in product-based environments, there are normally a mix of projects that are more monolithic in nature (i.e., that would align to “Rocks” and “Boulders”).  Sprints within iterative projects (for a given product team) would likely align to “Pebbles” in the above model and the question would be how to align the outcome of retrospectives into the overall governance model, which will be addressed below.

So, coming back to the diagram, for the purposes of illustration, the assumption we will use is that the portfolio we’re supporting is a mix of all four project types (the “Portfolio Makeup” at right above), so that we can discuss how the governance can be layered and integrated across the different categories expressed in the model itself.

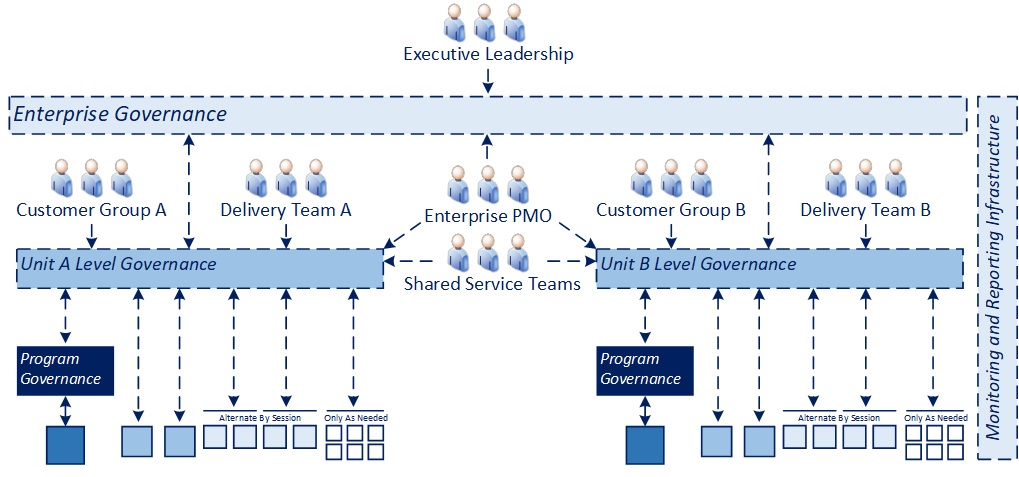
For the remainder of this article, we will assume the work in the delivery portfolio is divided equally between two business customer groups (A and B), with delivery teams supporting each as represented in the below diagram.

If your individual scenario involved a common customer, the model below could be simplified to one branch of the two represented.  If there were multiple groups, it could be scaled horizontally (adding branches for each additional organization) or if there were multiple groups across various geographies, it could be scaled by replicating and sizing the entire structure by entity (e.g., work organized by country in a global organization or by operating company in a conglomerate with multiple OpCos) and then adding one additional later for enterprise or global governance.

Key Dimensions

There are many dimensions to consider in establishing an enterprise delivery governance model.  The following breakdown is not intended to be exhaustive, but rather to highlight some key concepts that I believe are important to consider when designing the operating model for an IT organization.

General Design Principles

  • The goal is to enable decisions as close to the delivery as possible to improve efficiency and minimize the amount of “intervention” needed, unless it is a matter of securing additional resources (labor, funding, etc.) or addressing change control issues
  • The model should leverage a common operating infrastructure to the extent possible, to enable transparency and benchmarking across projects and portfolios. The more consistency and the more “plug and play” the infrastructure for monitoring and governance is, the faster (and more cost-effectively) projects and programs can typically be kicked off and accelerated into execution without having to define these processes independently
  • Metrics should move from summarized to more detailed as you move from oversight to execution, but the ability to “’drill down” should ideally be supported, so there is traceability

Business and IT PMOs versus “One” consolidated model

  • There is a proverbial question as to whether it is better to have “one”, integrated PMO construct, or an IT PMO separate from one that manages business dependencies (whether centralized or distributed)
  • From my perspective, this is a matter of scale and complexity. For smaller organizations, it may be efficient and practical to run everything through the same process, but as work scales, my inclination would be to separate concerns to keep the process from becoming too cumbersome and leverage the issue and risk management infrastructure to track and manage items relevant to the technology aspects of delivery.  There should be linkage and coordination to the extent that parallel organizations exist, but I would generally operate them independently so they can focus on their scope of concerns and be as effective as possible

Portfolio Management Integration

  • I’m assuming that portfolio management processes would operate “upstream” of the governance process and inform which projects are being slotted, address overall resource management and utilization, and release strategy
  • To the extent that change control in the course of delivery affects a planned release, a reverse dependency exists from the governance process back to the portfolio management process to see if schedule changes necessitate any bumping or reprioritization because of resource contention or deployment issues

IT Operations Integration

  • The infrastructure used to track and monitor delivery should come via the IT Operations capability, theoretically connecting at the IT Scorecard for executive level delivery metrics to portfolio and project metrics tracked at the execution level
  • IT Operations should own (or minimally help establish) the standards for reporting across the entire operating model

Participation

  • IT Operations should facilitate centralized governance processes as represented in the “Unit-level” and “Enterprise” governance processes in the diagram above. Program-level governance for “Boulders” would likely be best run by the delivery leadership accountable for those efforts
  • Participation should include whoever is needed to engage and resolve 80% (anecdotally) of the issues and risks that could be raised, but be limited to only people who need to be there
  • Governance processes should never be a “visibility” or “me too” exercise, they are a risk management and issue resolution activity, meant to drive engagement and support for delivery. Notes and decisions can and should be distributed to a broader audience as appropriate so additional stakeholders are informed
  • In the context of a RACI model (Responsible, Accountable, Consulted, Informed), meetings should include only “R” and “A” parties, who can reach out to extended stakeholders as needed (“C”), but very rarely anyone who would be defined as an “I” only
  • It is very easy to either overload a meeting to the point it becomes ineffective or not include the right participants to the extent it doesn’t accomplish anything, so this is a critical consideration for making a governance model effective

Session Scope and Scheduling

  • I’ve already addressed participation, but scheduling should consider the pace and criticality of interventions. Said differently, a frequent, recurring process may make sense when there is a significant volume of work, but something more episodic if there are a limited number of major milestones over the course of time where it makes sense to review progress and check in at specific points in time
  • Where an ongoing process is intended, “Boulders” and “Rocks” should have a standing spot on the agenda given the criticality and risk profiles of those efforts likely would be high. For “Pebbles”, some form of rotational involvement might make sense, such as including two of the four projects in the example above in every other meeting, or prioritizing any projects that are showing a Yellow or Red overall project health.  In the case of the “Sand”, those projects likely are so low risk that, beyond reporting some very basic operating metrics, they should only be included in a governance process when there is an issue that requires intervention or a schedule change that involves potential downstream impacts

Governance Processes

  • I mentioned this in concert with the example portfolio structure above, but it is important to consider tailoring the governance approach to the type of work so as not to create a cumbersome or bureaucratic environment for delivery teams where they focus on reporting and not managing and delivering their work
  • Compliance and security projects, as an example, are different than AI, modernization, or other types of efforts and should be reviewed with that in mind. To the extent a team is asked to provide a set of information as input to a governance process that doesn’t align cleanly to what they are doing, it becomes a distraction that creates no value.  That being said, there should be some core indicators and metrics that are collected regardless of the project type and reviewed consistently (as will be discussed in the next dimension)
  • The process should be designed and managed by IT Operations so it can be leveraged across an organization. While individual nuances can be applied that are specific to a particular delivery organization, it is important to have consistency to enable enterprise-level benchmarking and avoid the potential biases that can come from teams defining their own standards that could limit transparency and hinder effective risk management

Delivery Health and Metrics

  • I’ve written separately on Health and Transparency, but minimally every project should maintain a Red, Yellow, Green on Overall Health, and a second-level indicator on Schedule, Scope, Cost, Quality, and Resourcing that a project/program manager could supply very easily on an ongoing basis. That data should be collected at a defined interval to enable monitoring and inform governance processes on an ongoing basis, regardless of other quantitative metrics gather
  • Metrics on financials, resourcing, quality, issues, risks, and schedule can vary, but to the extent they can be drawn automatically from defined system(s) of record (e.g., MS Project, financial systems, a time tracking system with defined project coding, defect or incident management tools), the level of manual intervention required to enable governance should ideally be limited to data teams should be utilizing on an ongoing basis
  • In the event that there are multiple systems in place to track ongoing work, the IT Operations team should work with the delivery stakeholders to identify any enterprise-levels standards required to normalize them for reporting and governance purposes. To give a specific example, I encountered a situation once where there were five different defect management systems in place across a highly diversified IT organization.  In that case, the team developed a standard definition of how defects would be tracked and reported and the individual systems of record were mapped to that definition so that reporting was consistent across the organization

Change Control

  • Change is a critical area to monitor in any governance process because of the potential impact it has to resource consumption (labor, financials), customer delivery commitments, and schedule conflicts with other initiatives
  • Ideally a governance process should have the right information available to understand the implications of change as and when it is being reviewed as well as the right stakeholders present to make decisions with that information having been provided
  • To the extent that schedule, financial, or resource considerations change, information would need to be sent back to the IT Portfolio Management process to remedy any potential issues or disruptions that have been caused through decisions made. This is consistently missed in my experience in large delivery portfolios

Issue and Risk Management

  • Leveraging a common issue and risk management infrastructure both promotes a consistent way to track and report on these things across delivery efforts, but also creates a repository of “learnings” that could be reviewed and harvested in the interest of evaluating the efficacy of different approaches taken for similar issues/risks and promoting delivery health over time

Dependency/Integrated Plan Management

  • There are two dimensions to consider when it comes to dependencies. First is whether they exist within a project/program or are a dependency from that effort to others in the portfolio or downstream of it.  Second is whether the dependency is during the course of effort or connected to the delivery/deployment of the project
  • In my experience, teams are very good at covering project- or program-driven dependencies, but there can be major gaps in looking across delivery efforts to account for risks caused when things change. To that end, some level of dependency-related matrix should exist to identify and track dependencies across delivery efforts separate from a release calendar that focuses solely on deployment and “T-minus” milestones as projects near deployment
  • Once these dependencies are being tracked, changes that surface through the governance process can be escalated back to the IT Portfolio Management process and other delivery teams to understand and coordinate any adjustments required
  • This can include situations where there are sequential dependencies, as an example, where a schedule overrun requires additional resource commitment from a critical resource needed to kick off or participate in another delivery effort. Without a means to identify these dependencies, the downstream effort may be delayed or not have time to explore alternate resourcing options without having a ripple effect to that downstream delivery.  This is part of the argument for leveraging named resource planning (versus exclusively FTE-/role-based) for critical resources when slotting during the portfolio management process

Partner/Vendor Management

  • The IT Operations function should ideally help ensure that partners leverage internal reporting mechanisms or minimally conform to reporting standards and plug into existing governance processes where appropriate to do so
  • In the case of “Rocks” and “Boulders” that are largely partner-driven they likely will have a standalone governance process that leverages whatever process the partner has in place, but the goal should be to integrate and leverage whatever enterprise tools and standards are in place so that work can be benchmarked across delivery partners and also to compare the service delivery to internally-led efforts as well
  • It is very tempting to treat sourced work differently than projects delivered internal to IT, but who delivers a project should be secondary to whether the project is delivered on time, with quality and meets its objectives. The standards of excellence should apply regardless of who does the work

Learnings and Best Practices

  • Part of the potential benefit for having a shared infrastructure for executing governance discussions by comparison with distributing the work is that it enables you to see patterns in delivery, consistent bottlenecks, risks, and delays, and to leverage those learnings over time to improve delivery quality and predictability
  • Part of the governance process itself can also include having teams provide a post-mortem on their delivery efforts upon completion (successful or otherwise) so that other teams that participate in the governance process and the broader governance team can leverage those insights as appropriate

Change Management

  • While change management isn’t an explicit focus of a PMO/governance model, the dependency management surrounding deployment and learnings coming from various deployments should be coordinated with larger change management efforts and inform them on an ongoing basis in the interest of promoting more effective integration of new capabilities

Some Notes on Product Teams/Agile/SAFe Integration

  • It is tempting to treat product teams as isolated, independent, and discrete pieces of delivery. The issue with moving fully to that concept is that it becomes easy to lose transparency and benchmarking across delivery efforts that surface opportunities to more effectively manage risks and issues outside a given product/delivery team
  • To that end, part of the design process for the overall governance model should look at how to leverage and/or integrate the tooling for Agile projects with other enterprise project tracking tools as needed, along with integrating learnings from retrospectives with overall delivery improvement processes

Wrapping Up

Overall, there are many considerations that go into establishing an operating model for PMOs and delivery governance at end enterprise level.  The most important takeaway is to be deliberate and intentional about what you put in place, keep it light, do everything you can to leverage data that is already available, and keep the balance between the project and the portfolio in mind at all times.  The more project-centric you become, the more likely you will end up siloed and inefficient overall, and that will translate into missed dates, increased costs, and wasted utilization.

For Additional Information: On Health and Transparency, On Delivering at Speed, Making Governance Work, InBrief: IT Operations

Excellence doesn’t happen by accident.  Courageous leadership is essential.

Put value creation first, be disciplined, but nimble.

Want to discuss more?  Please send me a message.  I’m happy to explore with you.

-CJG 12/19/2025

InBrief: IT Operations

What It Is: IT Operations provides “IT for IT”, the infrastructure to track, monitor, and manage operating performance across various dimensions, depending on the scale and complexity of the organization

Why It Matters: The more an IT organization scales in headcount and complexity, the more important it becomes to have a way to benchmark performance and enable operational excellence

Key Concepts

  • IT Ops is a support organization meant to promote effectiveness, not create bureaucracy
  • Ops should be centralized regardless of the IT operating model (functional, product-based, etc.)
  • For large-scale organizations, a federated IT Ops model is preferable for overall org effectiveness

Key Dimensions

Transparency

  • Without visibility, it is nearly impossible to promote excellence and operational improvement
  • Focus should be on critical, minimum metrics that enable governance and benchmarking
  • Metrics can span from a leadership IT scorecard to portfolio and delivery metrics

Governance, Compliance, and Risk Management

  • IT Ops doesn’t need to provide PMO services, but it should ensure they exist and are effective
  • Compliance capabilities can be everything from regulatory and SOX to cyber security and audit

Portfolio Management

  • IT Ops may not provide the services, but should ensure that transparency and governance exist
  • Capabilities can span demand generation and prioritization to monitoring and value realization

Workforce and Sourcing Strategy

  • IT Ops should monitor internal/external performance, utilization, and workforce composition

Financial Management

  • IT Ops should help benchmark value/cost across IT at a service level and identify improvements

Continuous Improvement

  • IT Ops should identify and track operational excellence opportunities on an ongoing basis
  • Part of ongoing improvement should be reviewing and ensuring efficacy of IT services overall

For Additional Information: On Health and Transparency, Making Governance Work, Creating Value Through Strategy, Optimizing the Value of IT, On Managing Customer Relationships

Excellence doesn’t happen by accident.  Courageous leadership is essential.

Put value creation first, be disciplined, but nimble.

Want to discuss more?  Please send me a message.  I’m happy to explore with you.

– CJG 12/15/2025